
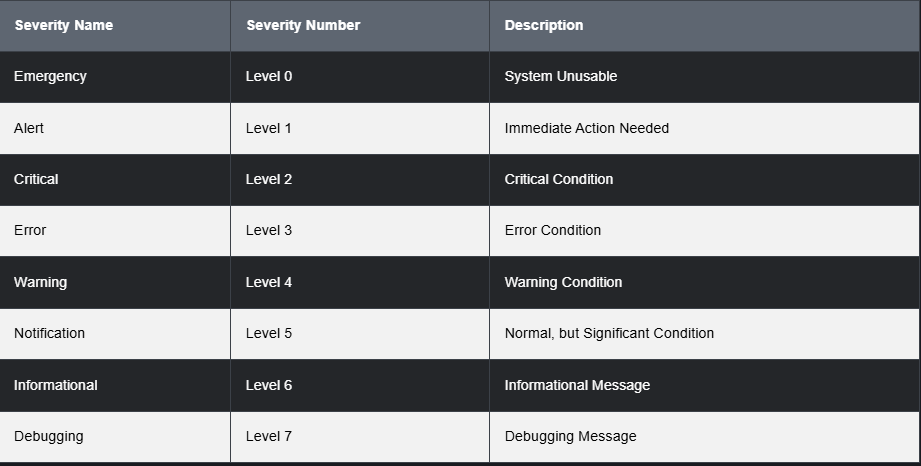
Every event is classified facility (which subsystem) + severity 0–7 (emergency → debug; “0 is worst, 7 is chattiest”), shipped to a central server over UDP/514 — or TCP/6514 with TLS when logs matter for compliance.
service timestamps log datetime msec localtime show-timezone
logging host 192.168.1.50 transport tcp
logging trap informational
logging source-interface Loopback0
logging rate-limit 100
Dependencies: NTP first — timestamps without a shared clock are fiction. UDP drops logs silently under load; debug-level logging in production burns CPU. Centralised logs = correlation across devices, which is the actual troubleshooting superpower; pair with SIEM ingest for security use.
Exam one-liners: syslog = push of events, SNMP = pull of counters. Severity 7 = debug.